
In 2026, security standards for software teams have rapidly shifted. Buyers, auditors, and internal risk leaders now expect developers to prevent common flaws before code reaches review. That shift makes training less optional and more operational.
Teams that ship web, mobile, and application programming interface features need practical habits for authentication, input handling, access control, dependency use, and error handling. The goal is simple: fewer defects, faster reviews, and safer releases.
Security teams cannot review every line before each release. Developers need enough context to spot risky patterns during normal work, especially in pull requests, feature planning, and defect triage. Practical secure coding training for developers helps teams connect common attack paths with daily coding choices, so fixes happen earlier and reviews become more focused.
Why Training Is Now a Release Requirement
Modern applications change often. New endpoints, payment paths, permissions, integrations, and data flows appear across every sprint. Each change can alter risk. A small access check mistake may expose records. Weak validation can turn a trusted field into an attack path.
Regulators and enterprise buyers now ask how teams prevent flaws, not just how they test after release. Evidence matters. A team may need to show training records, secure review steps, and repeatable standards. Without that proof, deals slow down and audits become harder.
Training also reduces friction between security and engineering. Developers gain shared language for risk, impact, and remediation. Security reviewers can spend less time explaining basics and more time investigating unusual behavior.
The Skills Developers Need Most
Effective instruction should match real engineering tasks. Theory helps, but developers need practice with vulnerable code, fixes, and review habits. The strongest programs focus on flaws that appear often and cause serious harm.
Input and Output Handling
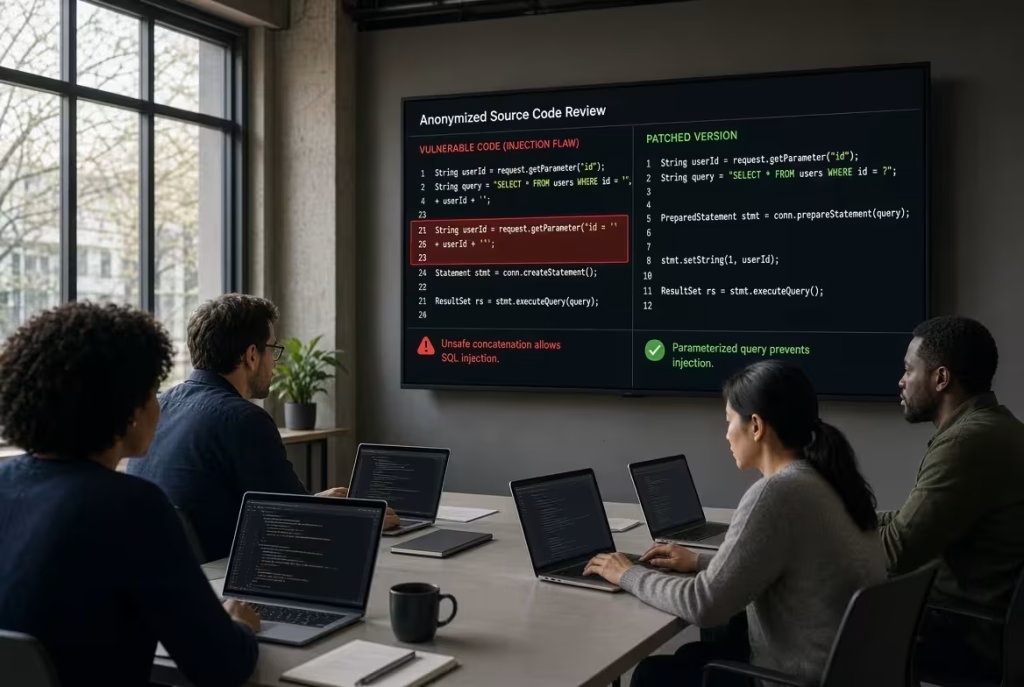
Injection flaws still appear because applications trust fields, headers, queries, and file content too early. Developers should learn parameterized queries, strict validation, safe encoding, and clear allow lists. These habits reduce risk across forms, search, reporting, and data import features.
Output handling matters too. A value may be safe in one context and unsafe in another. Training should explain how browser, database, command, and log contexts differ.
Authentication and Session Safety
Login systems create high-value targets. Developers need clear guidance on password storage, token lifetime, session renewal, reset flows, and multi-step verification. Small choices can weaken the full account model.
Teams should also practice abuse cases. Examples include replayed tokens, weak reset links, exposed session cookies, and missing rate controls.
Access Control and Business Logic
Access control defects often pass automated checks. A user may reach another account record by changing an identifier. A discount rule may apply outside its intended path. These issues require developer judgment.
Training should teach engineers to ask direct questions. Who owns this record? Which role may perform this action? Can the same action happen through another endpoint?
Why Annual Slides Are No Longer Enough
Traditional awareness sessions rarely change the code. Developers may remember policy language, yet still miss flaws during implementation. Better programs use short lessons, code exercises, and examples from the team’s stack.
Hands-on work builds memory. A developer who exploits a broken access check often recognizes the pattern later. Repairing the same flaw teaches why a patch works, not just where to place it.
Frequency also matters. One long session each year fades quickly. Short refreshers tied to new risks, release themes, or past findings keep security present without slowing delivery.
Measuring Training Impact
Training should produce evidence, not just attendance. Useful signals include fewer repeated findings, faster remediation, better pull request comments, and clearer threat notes in design tickets.
Security teams can track patterns across reviews. If injection findings drop but access issues rise, the next lesson should target authorization. Metrics should guide content, not punish engineers.
Managers should also compare defect timing. A flaw found during planning costs less than one found during testing. Earlier discovery shows that secure habits are moving into daily work.
Making Training Stick
The best programs fit existing routines. Teams can add short, secure design prompts to planning; review checklists to pull requests; and fix examples to internal notes. These practices make training easier to apply.
Leaders should give developers time to learn and repair issues well. Rushed teams often copy unsafe patterns because deadlines reward speed alone. Clear standards help engineers move quickly without guessing.
Security champions can reinforce the change. They translate guidance into local code patterns, answer questions, and spot recurring gaps before they spread.
Conclusion
Secure coding training has become a practical requirement because software risk now sits inside everyday engineering work. Developers need skills that match their code, release pressure, and review process.
Strong programs teach common flaws, attacker thinking, and reliable fixes through practice. They also create evidence for audits and buyers. Teams that invest in this capability reduce repeated defects, shorten remediation, and build security into delivery instead of treating it as a final gate.